
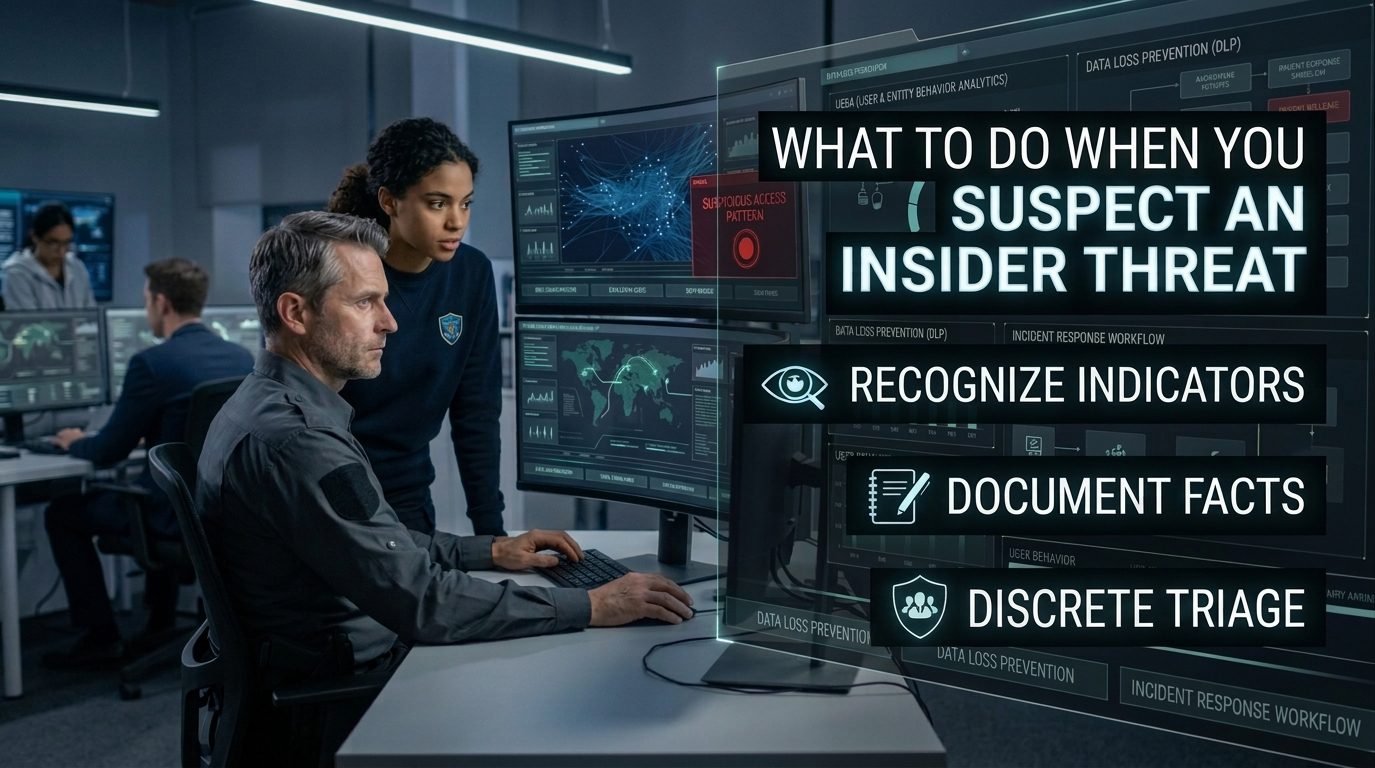
Discovering or suspecting that an employee, contractor, or business partner might be compromising company data is one of the most delicate challenges a manager will ever face. Unlike external cyberattacks, insider threats involve individuals who already hold valid access, understand your processes, and operate inside your trust boundary.
Whether the threat stems from simple negligence or deliberate malice, how you handle those initial moments of suspicion can make the difference between a swift resolution and an expensive regulatory, legal, or operational crisis.
Here is a practical, step by step roadmap on how to identify the warning signs, take discreet immediate action, and avoid common investigative pitfalls.
1. Differentiate Between Negligence and Malice
Before taking action, it helps to remember that not all insider threats are malicious actors looking to sell trade secrets. In fact, industry research shows that negligent actions account for over half of all insider security incidents:
- The Negligent Insider: An employee using unauthorized personal cloud storage (e.g., personal Google Drive or Dropbox) to work from home, clicking a phishing link, or accidentally sharing a folder publicly.
- The Malicious Insider: Someone intentionally exfiltrating intellectual property, financial data, or customer PII which is often motivated by impending departure, financial stress, or disgruntlement.
- The Compromised Insider: A legitimate user whose credentials or workstation have been hijacked by external attackers or state sponsored remote worker schemes.
Your initial approach should always focus on fact gathering rather than accusation, as most red flags initially look ambiguous.
2. Key Indicators to Watch For
While no single indicator equals guilt, a combination of behavioral and technical shifts warrants closer attention:
Behavioral Red Flags
- Out-of-Scope Interest: Asking detailed questions about projects, client databases, or financial systems that have no bearing on their daily duties.
- Unusual Work Shifts: Consistently accessing systems during off hours, over weekends, or while officially on annual leave without a clear operational reason.
- Visible Disgruntlement: Open hostility regarding performance reviews, skipped promotions, or upcoming restructuring; especially when paired with resignation rumors.
- Bypassing Controls: Repeatedly seeking workarounds for standard security controls (e.g., requesting security software exceptions or pushing to use unapproved SaaS apps).
Technical Red Flags
- Data Hoarding: Sudden spikes in file downloads, export activities, or printing of sensitive files.
- External File Transfers: Sending emails with heavy attachments to personal accounts or uploading bulk archives to unsanctioned cloud storage.
- Unusual Login Activity: Simultaneous logins from disparate geographic locations or unexpected VPN usage patterns.
3. The Immediate Response Protocol: 3 Golden Rules
If you suspect an employee or contractor may be exfiltrating data or misusing access, follow these three essential steps immediately:
Rule 1: Maintain Strict Confidentiality
Do not discuss your suspicions with team members, peers, or the employee in question. Tipping off a malicious insider often accelerates data exfiltration, causes evidence destruction, or prompts log wiping before security teams can preserve digital artifacts.
Rule 2: Document Objective Facts Only
Start an objective log of what you have observed. Avoid emotional language, guesswork, or character judgments. Stick strictly to demonstrable facts:
- Dates and exact times of unusual behavior or system access.
- Specific file or directory names involved, if known.
- Context: Notable events preceding the behavior (e.g., performance feedback meetings, notice of departure).
Rule 3: Engage the Core Triage Triad Discreetly
Reach out directly to a minimal group consisting of:
- Information Security / IT Lead: To initiate background log preservation and discreet monitoring without alerting the user.
- Human Resources: To ensure company policies and employee rights are followed.
- Legal / Risk Management: To review potential compliance, regulatory, or intellectual property implications.
4. What NOT to Do: Common Pitfalls
When suspicion arises, impulse reactions can severely complicate the situation. Avoid these common mistakes:
- Do NOT conduct a “rogue investigation”: Do not log into the employee’s machine yourself, search their desk, or attempt to inspect personal devices. Uncoordinated actions can contaminate digital evidence, rendering it inadmissible in court or internal disciplinary proceedings.
- Do NOT confront the person prematurely: Accusing an employee without verified technical evidence damages trust if you are wrong and triggers immediate cover-ups if you are right.
- Do NOT immediately revoke access without alignment: Abruptly cutting off accounts outside an agreed HR/Legal plan alerts the individual immediately and may prevent security analysts from capturing real time forensic proof.
- Do NOT treat mistakes like sabotage: If investigation reveals the issue was an accidental policy bypass, treat it as a coaching and process enforcement opportunity rather than a punitive interrogation.
5. How Security and HR Teams Verify Suspicion
Once leadership, HR, and Security align, technical controls allow for discreet verification:
- Log & Forensic Preservation: Security teams quietly preserve network logs, email records, and audit trails under legal hold before any retention policies overwrite them.
- User & Entity Behavior Analytics (UEBA): Analyzing baseline activity against recent anomalies to confirm whether file transfers or access spikes deviate significantly from historical norms.
- Structured Offboarding: If the investigation validates intentional misconduct or risk, HR and IT coordinate a synchronized termination protocol; instantly revoking access across Single Sign-On (SSO), VPNs, and cloud storage the exact moment the exit discussion begins.
6. Proactive Prevention: Reducing Future Risk
The best way to manage insider threats is to minimize the opportunity for them to occur in the first place:
- Enforce Least Privilege Access: Audit file permissions quarterly to ensure team members only access what they strictly need.
- Automate Provisioning & Deprovisioning: Ensure employee accounts and cloud accesses are disabled immediately upon departure.
- Create Non-Punitive Reporting Channels: Give employees a simple, anonymous way to report suspicious activity or security mistakes without fear of immediate retaliation.
Final Thoughts
Handling a suspected insider threat requires a balanced mix of discretion, objective documentation, and cross-functional coordination. By staying calm, avoiding premature confrontation, and involving HR, Legal, and IT early, leaders can protect company assets while upholding a fair and professional work environment.
Leave a Reply